Vendor Risk, Fake Automation, and the Green Check Trap
A vendor questionnaire is not vendor risk management. It’s a starting point. Sometimes a useful one. But if your process ends with a filled-out form and a SOC report in a folder, you’re not managing risk — you’re documenting optimism. In this Get NIST-y, Jared and Mike use the Mythos supply chain mess to highlight […]
AI is Useful. AI Slop Is Not.
AI is everywhere right now — and if you’re running an MSP, you’re feeling it from every direction. Your PSA has AI. Your RMM has AI. Your documentation platform has AI. Your quoting tool probably has AI. At this point, we’re all just waiting for the coffee maker to start summarizing tickets. But here’s the […]
Blacksmith Wins 2026 Q1 Category Leader Award!
Blacksmith just earned another BetterTracker (Channel Program) Category Leader badge for 2026 Q1 — our latest quarter ranked among the top‑rated vendors in the IT channel across more than 80 technology categories. Blacksmith’s 2026 Q1 Category Win For 2026 Q1, Blacksmith was recognized as a Category Leader in Compliance. That means MSPs and IT providers […]
Higher‑Level Advisory Services Your MSP Should Be Monetizing
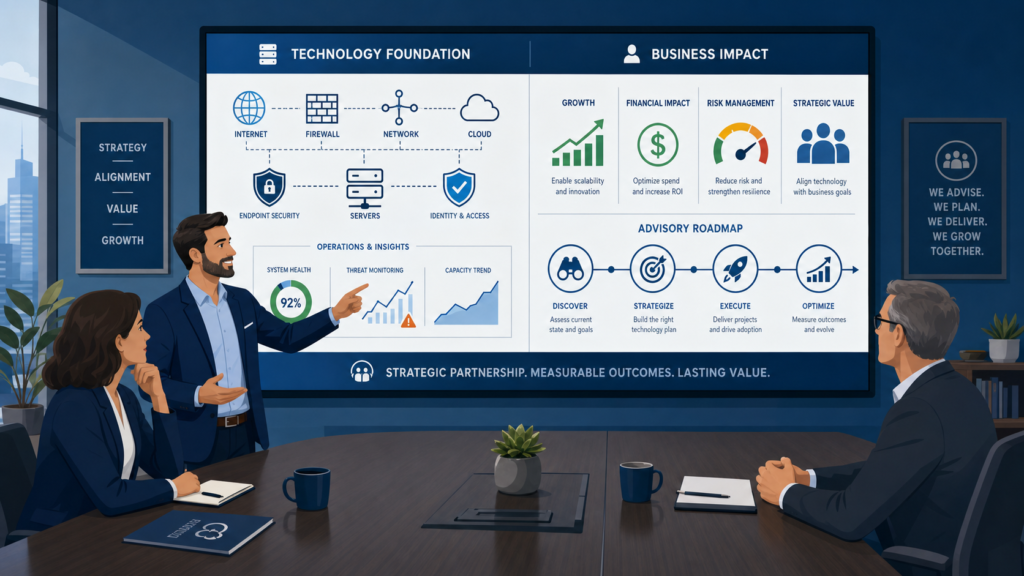
Most MSPs still sell themselves as “outsourced IT” or “24/7 support.” That message is increasingly out of step with what growth‑minded organizations actually want: a strategic partner who can turn technology into a lever for revenue, risk reduction, and scale. The good news is you’re already doing pieces of that work — you’re just not […]
Data as a Service: How MSPs Turn Noisy Logs into Business Insights
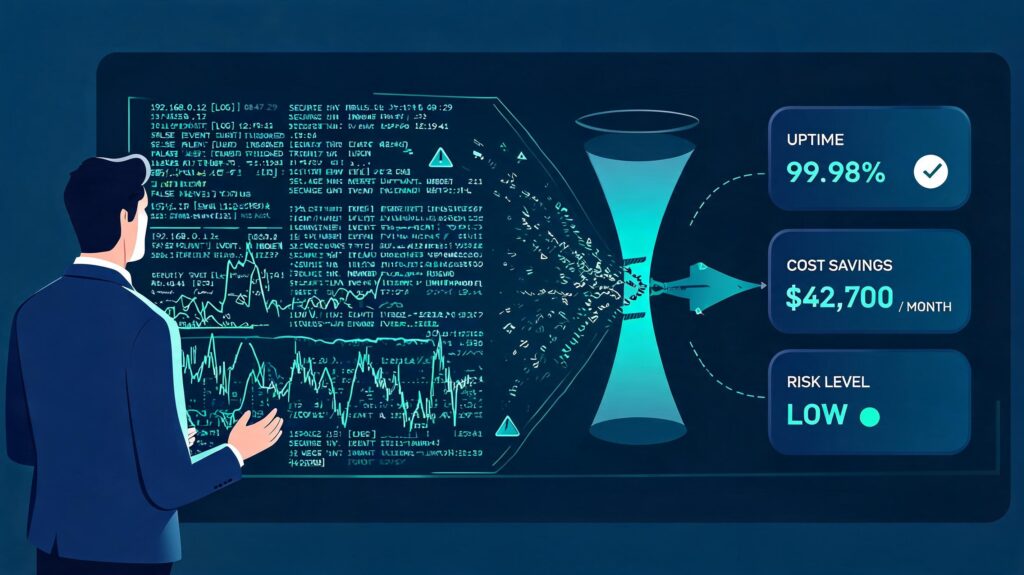
Small and mid‑sized businesses have more data than ever, but very little of it actually informs day‑to‑day decisions. Business intelligence (BI) platforms promise dashboards and data‑driven strategy, yet many SMEs either never deploy them fully, or they struggle with cost, complexity, and a lack of in‑house skills to make the tools pay off. Instead, executives […]
From “We Do Security” to Ransomware-Ready Compliance: How MSPs Turn Framework Jargon into Revenue and Risk Reduction
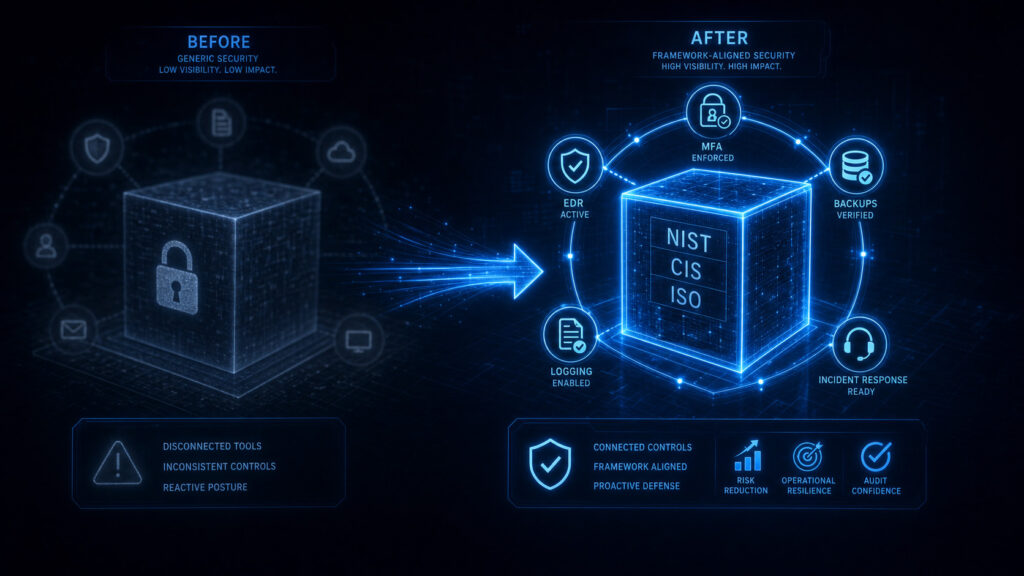
Buyers no longer accept “we do security” as an answer. They’re asking how security is implemented, whether it maps to recognizable frameworks, and if it is robust enough to satisfy insurers, auditors, and regulators when ransomware hits. This article walks through how to design a ransomware-ready stack that you can both operate and prove — […]
Incident Reporting Is Changing Faster Than Your Playbooks
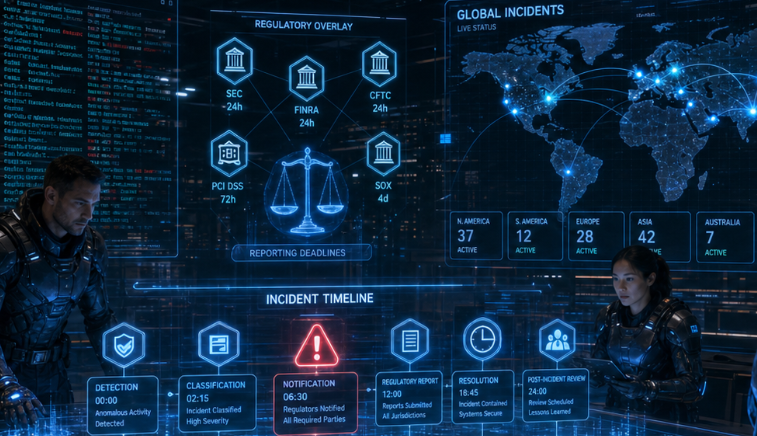
For MSPs and internal IT teams, incident response used to revolve around containment, eradication, recovery, and a long argument over whether anyone outside the company really needed to know. That era is over. In the last two years, cyber incident reporting has shifted from a loosely coordinated mix of breach notice laws and sector rules […]
Mythos, Vendor Risk, and the Supply Chain Problems MSPs Can’t Ignore
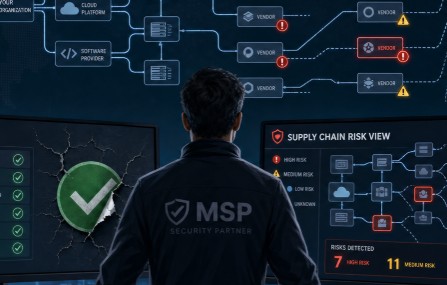
If the Mythos supply chain incident felt like somebody else’s problem, that feeling did not last long. The useful lesson for MSPs is not that one AI-related event made headlines, but that it exposed how quickly upstream vendor failures, weak access controls, and murky fourth-party relationships can become downstream operational risk for service providers and […]
Explain It or Don’t Ship It: Black-Box AI vs. Regulatory Transparency
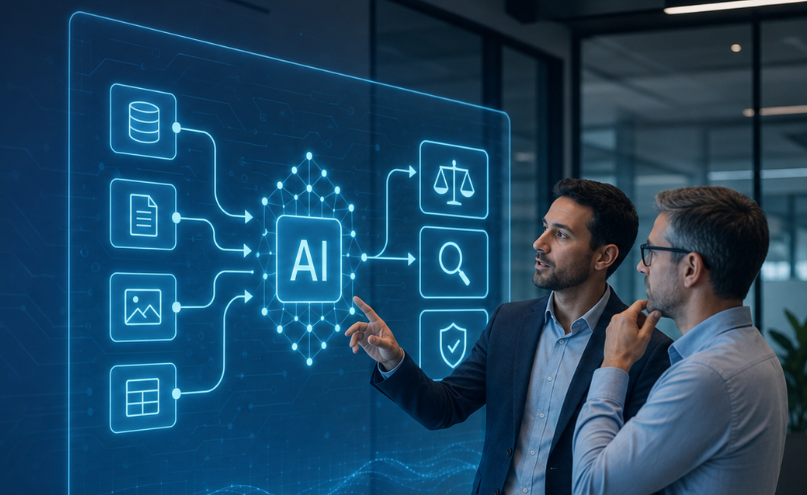
If you’ve ever had a customer ask, “Why did your system do that?” and felt your stomach drop, AI is about to make that feeling a lot more common. As more businesses plug AI into decisions about money, jobs, and risk, regulators and customers are all quietly agreeing on one new rule: if you can’t […]
Unauthenticated and Unforgiving: Why 2026’s RCE Wave Is Different
If 2025 was the year of record CVE volume — 48,185 published, up 20% from 2024 — then 2026 is the year attackers stopped waiting for credentials. The latest MetInfo CMS exploitation proves it: CVE-2026-29014, a pre-auth PHP injection flaw (CVSS 9.8) in versions 7.9–8.1, went from disclosure to active attacks by April 25, surging […]