How MSPs Can Stop Compliance From Blowing Up Client Roadmaps (And Use It to Deepen the Relationship)
Business delivery runs on market deadlines. Compliance runs on regulatory mandates. MSPs live in the collision zone between those two clocks — and the ones who get ahead of it turn a constant source of pain into a structured, billable service. Two clocks, one MSP If you support regulated clients, you’ve seen this movie. Your […]
The MSP “Trust Surface”: Identity, VPNs, and Tenant Isolation as Your Real Perimeter
Most MSPs don’t get popped because of some cinematic zero‑day. They get popped because one technician’s credentials are phished, a shared VPN drops them into a flat client network, and their tools do exactly what they were designed to do — only under an attacker’s control. The real perimeter isn’t the firewall anymore; it’s your […]
From Break‑Fix to MDR‑First: What 2026 Threats Really Demand From MSP Stacks
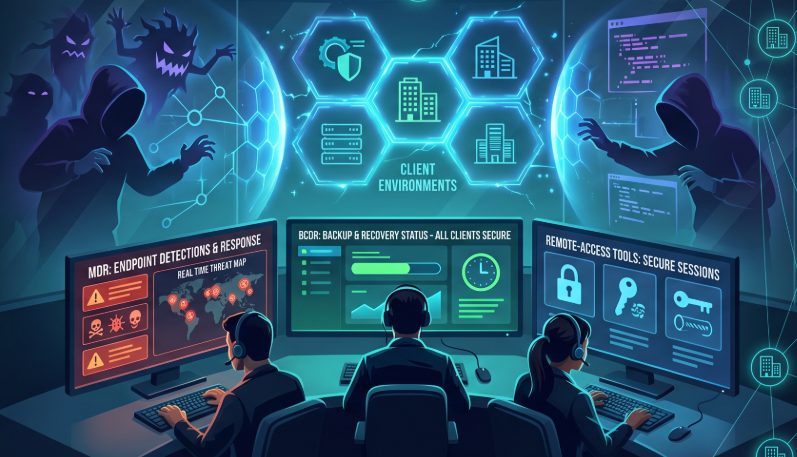
If you’re still leading with “unlimited support, AV, and backups” in 2026, you’re selling yesterday’s MSP. The threat landscape has shifted to identity abuse, remote‑access hijacking, and fast‑moving ransomware campaigns that treat your tools and your staff as the most efficient route into every client you touch. Security is no longer a bolt‑on SKU; it’s […]
AI and LLMs: Can MSPs Navigate This Compliance Maze?

Straight from Blacksmith: Listen to our discussion about compliant AI on Get NIST-y! AI and compliance are colliding in a very practical way for MSPs. On one hand, clients want the productivity boost from LLMs; on the other, regulators and insurers are watching closely. At the same time, the security programs you build […]
Cyber Insurance Risks, Client Questionnaires, and MSP Assumptions
Straight from Blacksmith: Listen to our discussion about these topics on Get NIST-y! When compliance goes sideways, it rarely does it quietly. For MSPs, a single “helpful” answer on an insurance form or a fuzzy interpretation of MFA can turn into real liability when something breaks — and that is exactly what this […]
The Axios npm Breach: 7 Supply Chain Lessons Every MSP Can Absorb Right Now
Straight from Blacksmith: Listen to our discussion about the Axios attack on Get NIST-y! Axios’ late‑March supply chain compromise turned one ubiquitous open‑source package into a delivery system for a cross‑platform RAT — and for managed service providers, it is a dress rehearsal for the next upstream software failure that ripples across every […]
What the Tinder / Match Group Breach Teaches About Real-World Compliance
The Tinder / Match Group incident is a near‑perfect case study for MSPs: a big brand, sensitive data, and an attack that rides through humans, identity, and SaaS sprawl instead of some exotic zero‑day. Used well, it can sharpen your own program and give you a concrete story to tell every SMB you serve. What […]
Designing a Low-Lift, Win-Win Compliance Engagement for MSP Clients
Designing a good compliance engagement is less about adding more tasks and more about changing the shape of the work so clients feel like they are telling a story, not doing homework. Done well, that structure also makes your delivery more consistent and scalable as an MSP. Why compliance feels like homework Most clients experience […]
5-Tier Risk Framework for Mitigating Human Error
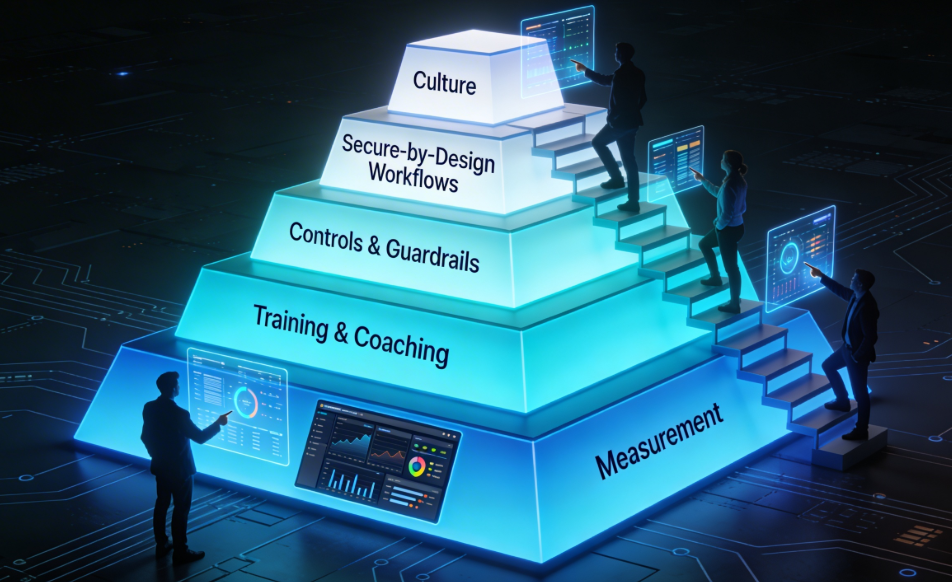
Most security incidents still start with a person: a rushed click, a reused password, a file sent to the wrong place. For years, the default answer has been “more awareness training,” but that treats every employee as the same level of risk and ignores the environment they work in. A better approach is to treat […]
OAuth Abuse Is the New Phishing: Why “Log In With X” Keeps Burning You
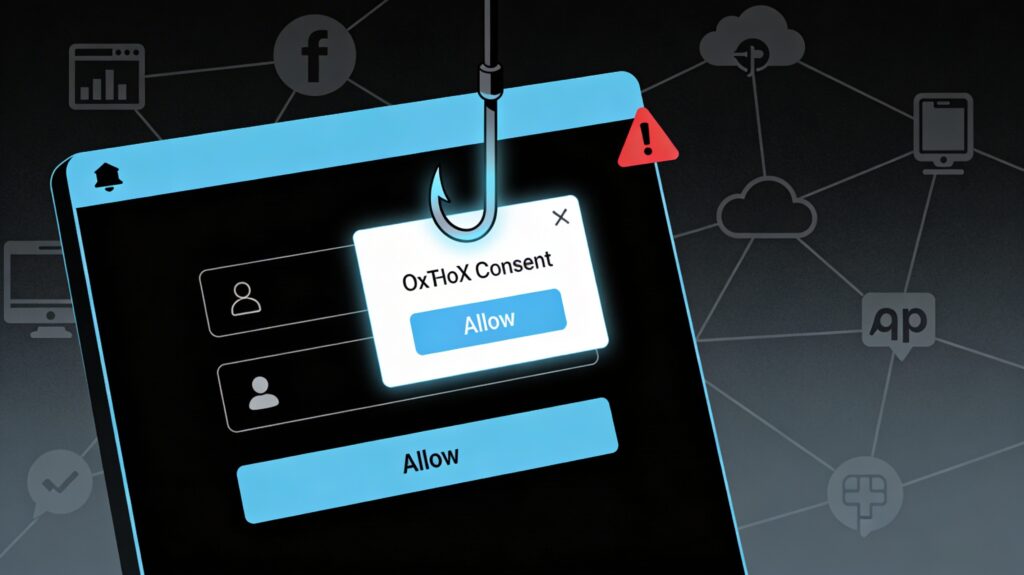
OAuth abuse has quietly become the phishing technique that slips past your MFA, your “security‑aware” users, and your cloud email filters. Recent campaigns abusing OAuth redirects and malicious apps in Microsoft Entra ID and Google Workspace show that “Log in with X” is now one of the easiest ways into your SaaS estate. Phishing Without […]