Get NIST-y Roundup: The Compliance Trap, the CMMC Monster, and the AI Wild West

Three episodes, one throughline: MSPs catch flak for the compliance decisions their clients refuse to make. This roundup pulls the practical takeaways from our latest run of Get NIST-y — the podcast where we skip the framework LARP and talk about what actually works in a client environment on a Tuesday afternoon. If you missed […]
Why AI Agents Are the Fastest-Growing Attack Surface Your MSP Isn’t Governing

Your clients are hiring a shadow workforce — Copilot Studio flows, Salesforce Einstein actions, n8n automations, coding assistants with tokens into production repos, MCP servers wired into internal data. They’re not paying it, not onboarding it, and mostly not telling you about it. BeyondTrust’s Phantom Labs clocked a 466.7% year-over-year jump in enterprise AI agents. […]
Cyber Risk Review: Phantom Squatting, Slopsquatting, and HalluSquatting
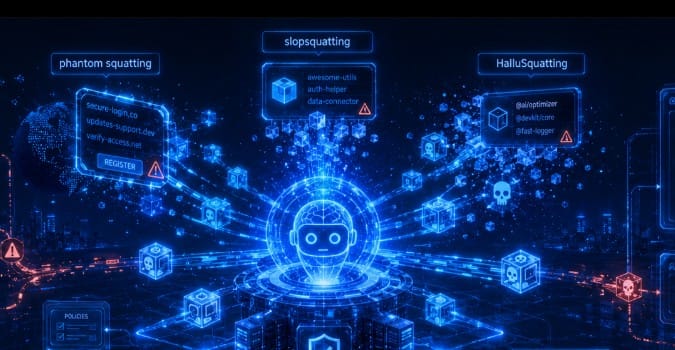
AI hallucinations are creating a new supply-chain problem for MSPs and the organizations they protect, and the threat has a few names worth remembering: phantom squatting for domains, slopsquatting for packages, and hallusquatting (HalluSquatting) as the broader pattern of weaponizing invented names and links. In the domain version, attackers register the fake web addresses that LLMs […]
Industry Pros Are Talking About the End of Human Pen Testing. Are They Right?
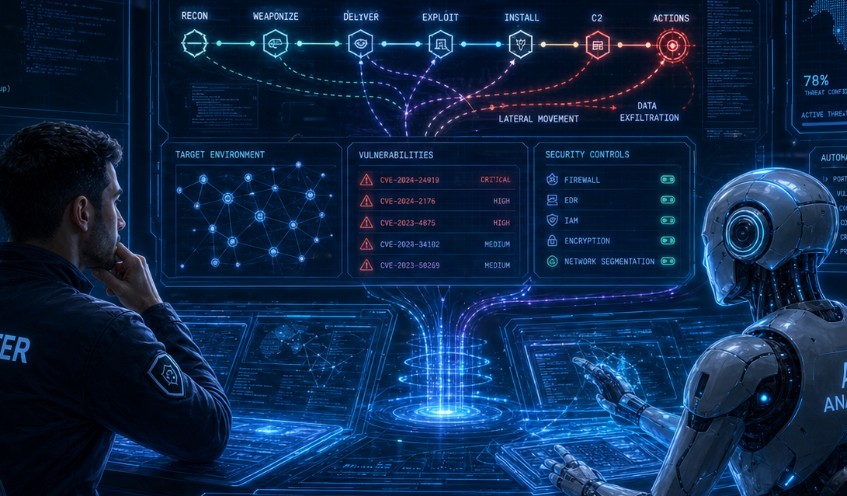
The “death of human pen testing” makes a great headline, but what we are really watching is the death of traditional pen testing: slow, point‑in‑time, human‑only engagements that cannot keep up with AI‑accelerated attack surfaces or modern compliance expectations. Automated and AI‑assisted testing will gut the old model — but they are far more likely to […]
Shadow AI Is Now Your Problem: Why Doubling Sensitive Data Uploads Should Keep MSPs Up at Night
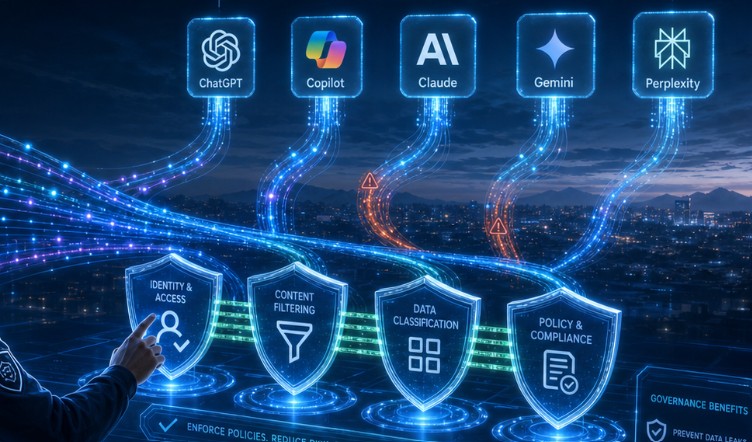
There has been a 93% year-over-year increase in employees transferring enterprise data to AI tools. — Zscaler 2026 AI Threat Report Managed service providers are quietly inheriting a new kind of data‑loss problem: clients’ employees are shoveling sensitive data into AI tools at a rate that has doubled in the last year, with the average […]
AI Is Finally Real Money for MSPs: Turning Hype into Billable Outcomes
The MSP conversation around AI has changed. In 2026, AI is no longer a novelty for demos, webinars, and investor decks; it is becoming a margin story, a service-delivery story, and a client-retention story. Recent MSP market analysis tied to Omdia’s 2026 outlook points to slower overall growth, more intense competition, and rising expectations around […]
AI is Useful. AI Slop Is Not.
AI is everywhere right now — and if you’re running an MSP, you’re feeling it from every direction. Your PSA has AI. Your RMM has AI. Your documentation platform has AI. Your quoting tool probably has AI. At this point, we’re all just waiting for the coffee maker to start summarizing tickets. But here’s the […]
Mythos, Vendor Risk, and the Supply Chain Problems MSPs Can’t Ignore
If the Mythos supply chain incident felt like somebody else’s problem, that feeling did not last long. The useful lesson for MSPs is not that one AI-related event made headlines, but that it exposed how quickly upstream vendor failures, weak access controls, and murky fourth-party relationships can become downstream operational risk for service providers and […]
Explain It or Don’t Ship It: Black-Box AI vs. Regulatory Transparency
If you’ve ever had a customer ask, “Why did your system do that?” and felt your stomach drop, AI is about to make that feeling a lot more common. As more businesses plug AI into decisions about money, jobs, and risk, regulators and customers are all quietly agreeing on one new rule: if you can’t […]
Agentic AI Is Already Expanding Your Attack Surface in 2026
The biggest risk with agentic AI isn’t what’s coming next. It’s what’s already here. Across organizations, AI agents are quietly moving from passive assistants to active participants. They’re writing code, querying internal systems, sending messages, and triggering workflows. Not in a lab. Not in a pilot. In production. Right now. And in many cases, security […]