Treat the SonicWall SMA 1000 Like an IdP: An MSP Playbook for the September Zero-Days
On September 1, 2026, SonicWall’s PSIRT disclosed two vulnerabilities in the SMA 1000 Series secure-remote-access appliances and confirmed they were already being exploited in the wild. The advisory says the quiet part out loud: “These vulnerabilities have been confirmed as being actively exploited in the wild.” CISA added both CVEs to the Known Exploited Vulnerabilities […]
“City-Forum” Campaign Quietly Harvests Salesforce and ServiceNow Data Through Guest-User Misconfigs — And MSPs Are on the Hook
A long-running threat campaign dubbed “City-Forum” has been systematically extracting data from Salesforce and ServiceNow tenants worldwide since at least March 2025 — without exploiting a single vulnerability. Every record was pulled through legitimate, unauthenticated endpoints that customers left overly permissive. If you manage a client’s Salesforce Experience Cloud site, Lightning Web Runtime portal, or […]
Local Government Cyberattacks Are Disrupting Public Services. MSPs Need to Prepare Now.
A recent string of cyber incidents has forced local governments in multiple states to shut down networks, interrupt public-facing services, and shift emergency operations to backup processes. For MSPs supporting municipalities, this is a reminder that ransomware recovery is not just an IT exercise — it can become a public-safety obligation. The incidents are not […]
Why Teams Vishing Just Became the Attack Surface Your Email Gateway Can’t See
Microsoft’s Q2 2026 Email Threat Landscape report, published July 23, delivered a striking pair of numbers: phishing tied to the Tycoon2FA platform collapsed 92% after a takedown operation, while weekly malicious Microsoft Teams call attempts are now running at nearly ten times their mid-2025 baseline. Weekly Teams vishing rose 31% from April to May, another […]
Cyber Risk Review: Phantom Squatting, Slopsquatting, and HalluSquatting
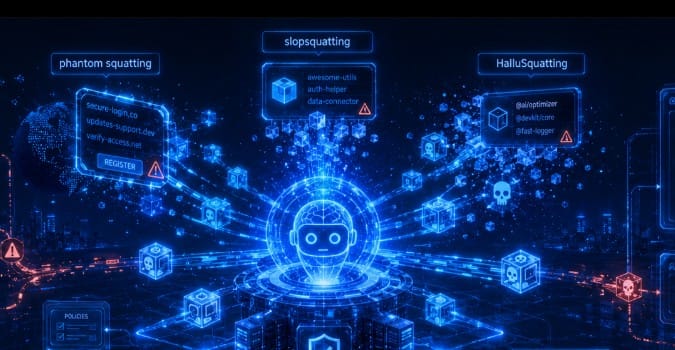
AI hallucinations are creating a new supply-chain problem for MSPs and the organizations they protect, and the threat has a few names worth remembering: phantom squatting for domains, slopsquatting for packages, and hallusquatting (HalluSquatting) as the broader pattern of weaponizing invented names and links. In the domain version, attackers register the fake web addresses that LLMs […]
ClickFix Is Winning Right Now. MSPs Need to Treat It Like a Tier-1 Delivery Threat
ClickFix has become one of the most noteworthy malware delivery methods in 2026 because it bypasses the normal technical choke points MSPs rely on and instead turns end users into the execution mechanism. Recent reporting indicates the technique dominated malware delivery in the March-May 2026 period and should no longer be treated as an emerging tactic […]
Mythos, Vendor Risk, and the Supply Chain Problems MSPs Can’t Ignore
If the Mythos supply chain incident felt like somebody else’s problem, that feeling did not last long. The useful lesson for MSPs is not that one AI-related event made headlines, but that it exposed how quickly upstream vendor failures, weak access controls, and murky fourth-party relationships can become downstream operational risk for service providers and […]
New York: Mass SMS Scam via Hijacked Alert Service
On November 10th, hackers exploited a legitimate mass texting service to send hundreds of thousands of scam messages — including to New York State’s official alert subscribers. This incident, which leveraged public trust in emergency messaging channels, marks an evolution in SMS phishing (“smishing”) scams and raises pressing concerns for individuals and organizations alike. What […]
CISA Flags Rapid7 Velociraptor Vulnerability as Active Ransomware Target
A critical vulnerability in Rapid7’s Velociraptor — tracked as CVE-2025-6264 — has recently been highlighted by the Cybersecurity and Infrastructure Security Agency (CISA), underscoring new risks faced by organizations relying on security tools for endpoint monitoring and threat hunting. The flaw, now included in CISA’s Known Exploited Vulnerabilities catalogue, has become a key target for […]
Exploring the October 2025 Discord Data Leak
In early October 2025, Discord disclosed a significant data breach that exposed confidential user data through a compromise at a third-party customer support provider. This incident has triggered renewed concerns about supply chain security and the risks associated with trusted external vendors in today’s interconnected IT ecosystem. The breach not only affected Discord’s own systems […]