Why MSPs Fall Behind on Compliance Management
MSP compliance management sits at the intersection of expanding regulations and limited operational capacity. Every new framework your clients fall under adds documentation, controls, and audit cycles to your plate. This article breaks down the root causes behind these operational bottlenecks and shows how a Compliance-as-a-Service model can reduce your team’s workload. Blacksmith InfoSec helps […]
Get NIST-y Roundup: The Compliance Trap, the CMMC Monster, and the AI Wild West

Three episodes, one throughline: MSPs catch flak for the compliance decisions their clients refuse to make. This roundup pulls the practical takeaways from our latest run of Get NIST-y — the podcast where we skip the framework LARP and talk about what actually works in a client environment on a Tuesday afternoon. If you missed […]
The Checkbox Isn’t the Point: Does Speed Undermine Compliance Credibility?
A new piece of research landed recently that should make any MSP concerned with cybersecurity and compliance stop and think. According to a June 2026 study⁽¹⁾ by business resilience specialists IO — conducted among 251 senior UK cybersecurity managers — 87% of respondents believe the speed at which compliance certification is achieved affects its credibility . […]
Vendor Risk, Fake Automation, and the Green Check Trap
A vendor questionnaire is not vendor risk management. It’s a starting point. Sometimes a useful one. But if your process ends with a filled-out form and a SOC report in a folder, you’re not managing risk — you’re documenting optimism. In this Get NIST-y, Jared and Mike use the Mythos supply chain mess to highlight […]
Higher‑Level Advisory Services Your MSP Should Be Monetizing
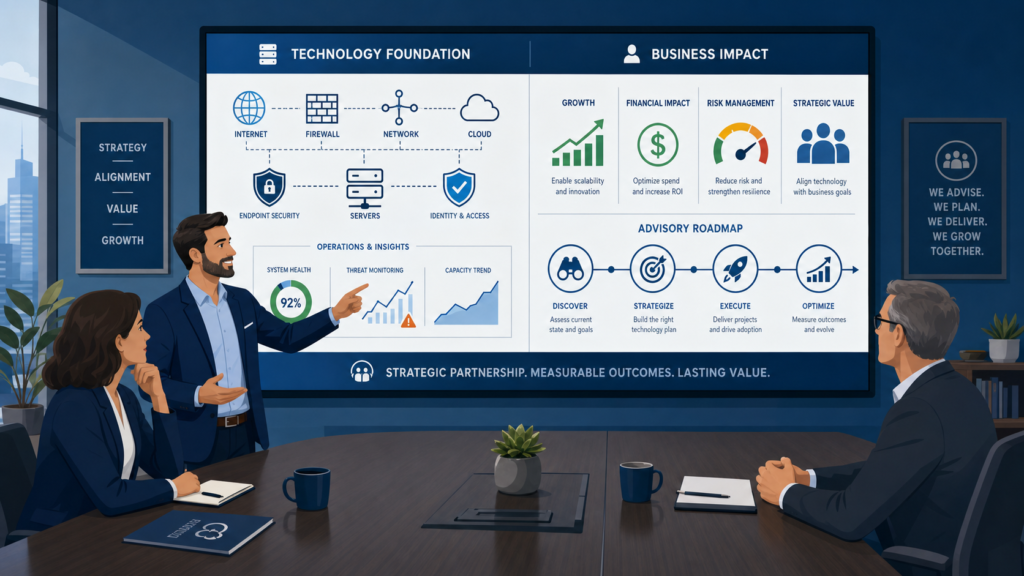
Most MSPs still sell themselves as “outsourced IT” or “24/7 support.” That message is increasingly out of step with what growth‑minded organizations actually want: a strategic partner who can turn technology into a lever for revenue, risk reduction, and scale. The good news is you’re already doing pieces of that work — you’re just not […]
The MSP “Trust Surface”: Identity, VPNs, and Tenant Isolation as Your Real Perimeter
Most MSPs don’t get popped because of some cinematic zero‑day. They get popped because one technician’s credentials are phished, a shared VPN drops them into a flat client network, and their tools do exactly what they were designed to do — only under an attacker’s control. The real perimeter isn’t the firewall anymore; it’s your […]
When 3,322 Breaches Is “Normal”: Why Boards Are Failing Cyber Governance
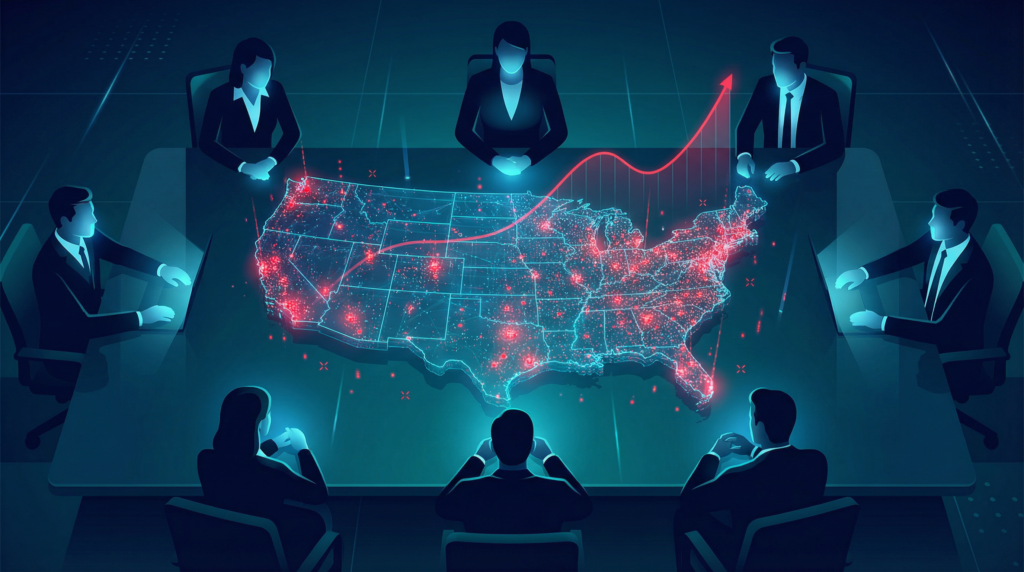
In 2025, the United States set a new record: 3,322 reported data compromises in a single year. That is not a typo, and it is not an outlier — it is the third year in a row with more than 3,000 incidents and a 79% increase in breaches over the past five years. For all […]
Cyber Insurance Risks, Client Questionnaires, and MSP Assumptions
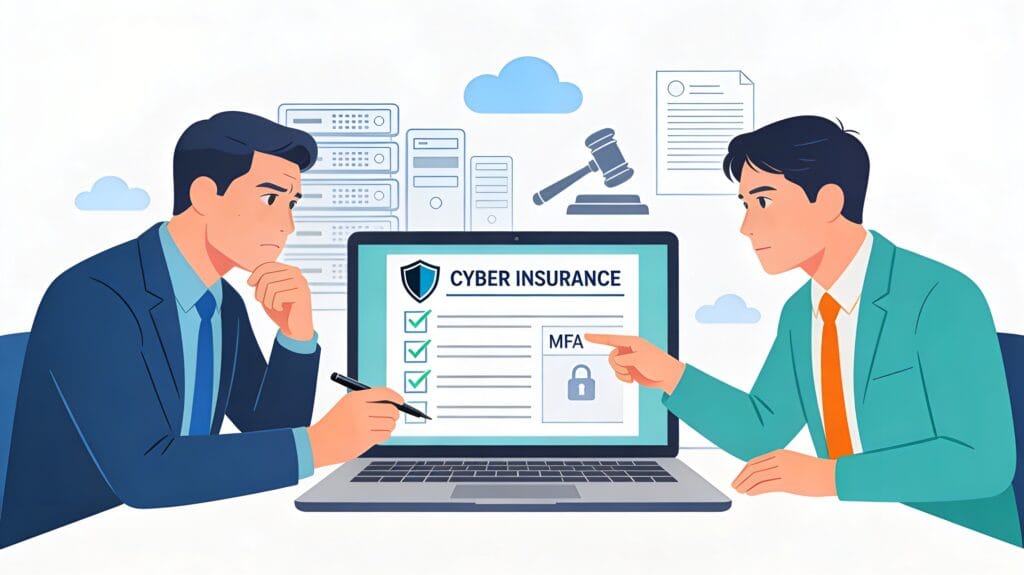
Straight from Blacksmith: Listen to our discussion about these topics on Get NIST-y! When compliance goes sideways, it rarely does it quietly. For MSPs, a single “helpful” answer on an insurance form or a fuzzy interpretation of MFA can turn into real liability when something breaks — and that is exactly what this […]
Whoops! What We Can Learn from South Korea’s $4.8m Crypto Key Blunder
Officials in South Korea’s National Tax Service stood behind a table of seized hardware wallets prepping for their victory lap — cameras rolling, proud to show the public that crypto‑enabled tax dodging had consequences. The photos went out in high resolution. On social media, people zoomed in — and found the handwritten seed phrase for […]
OAuth Abuse Is the New Phishing: Why “Log In With X” Keeps Burning You
OAuth abuse has quietly become the phishing technique that slips past your MFA, your “security‑aware” users, and your cloud email filters. Recent campaigns abusing OAuth redirects and malicious apps in Microsoft Entra ID and Google Workspace show that “Log in with X” is now one of the easiest ways into your SaaS estate. Phishing Without […]